Cloud Security
Cloud Security Misconfiguration and Identity Abuse: A Practical Defensive Guide
Learn how cloud security misconfiguration can expose resources, credentials and identity paths, and use a provider-neutral checklist for prevention, detection and response.
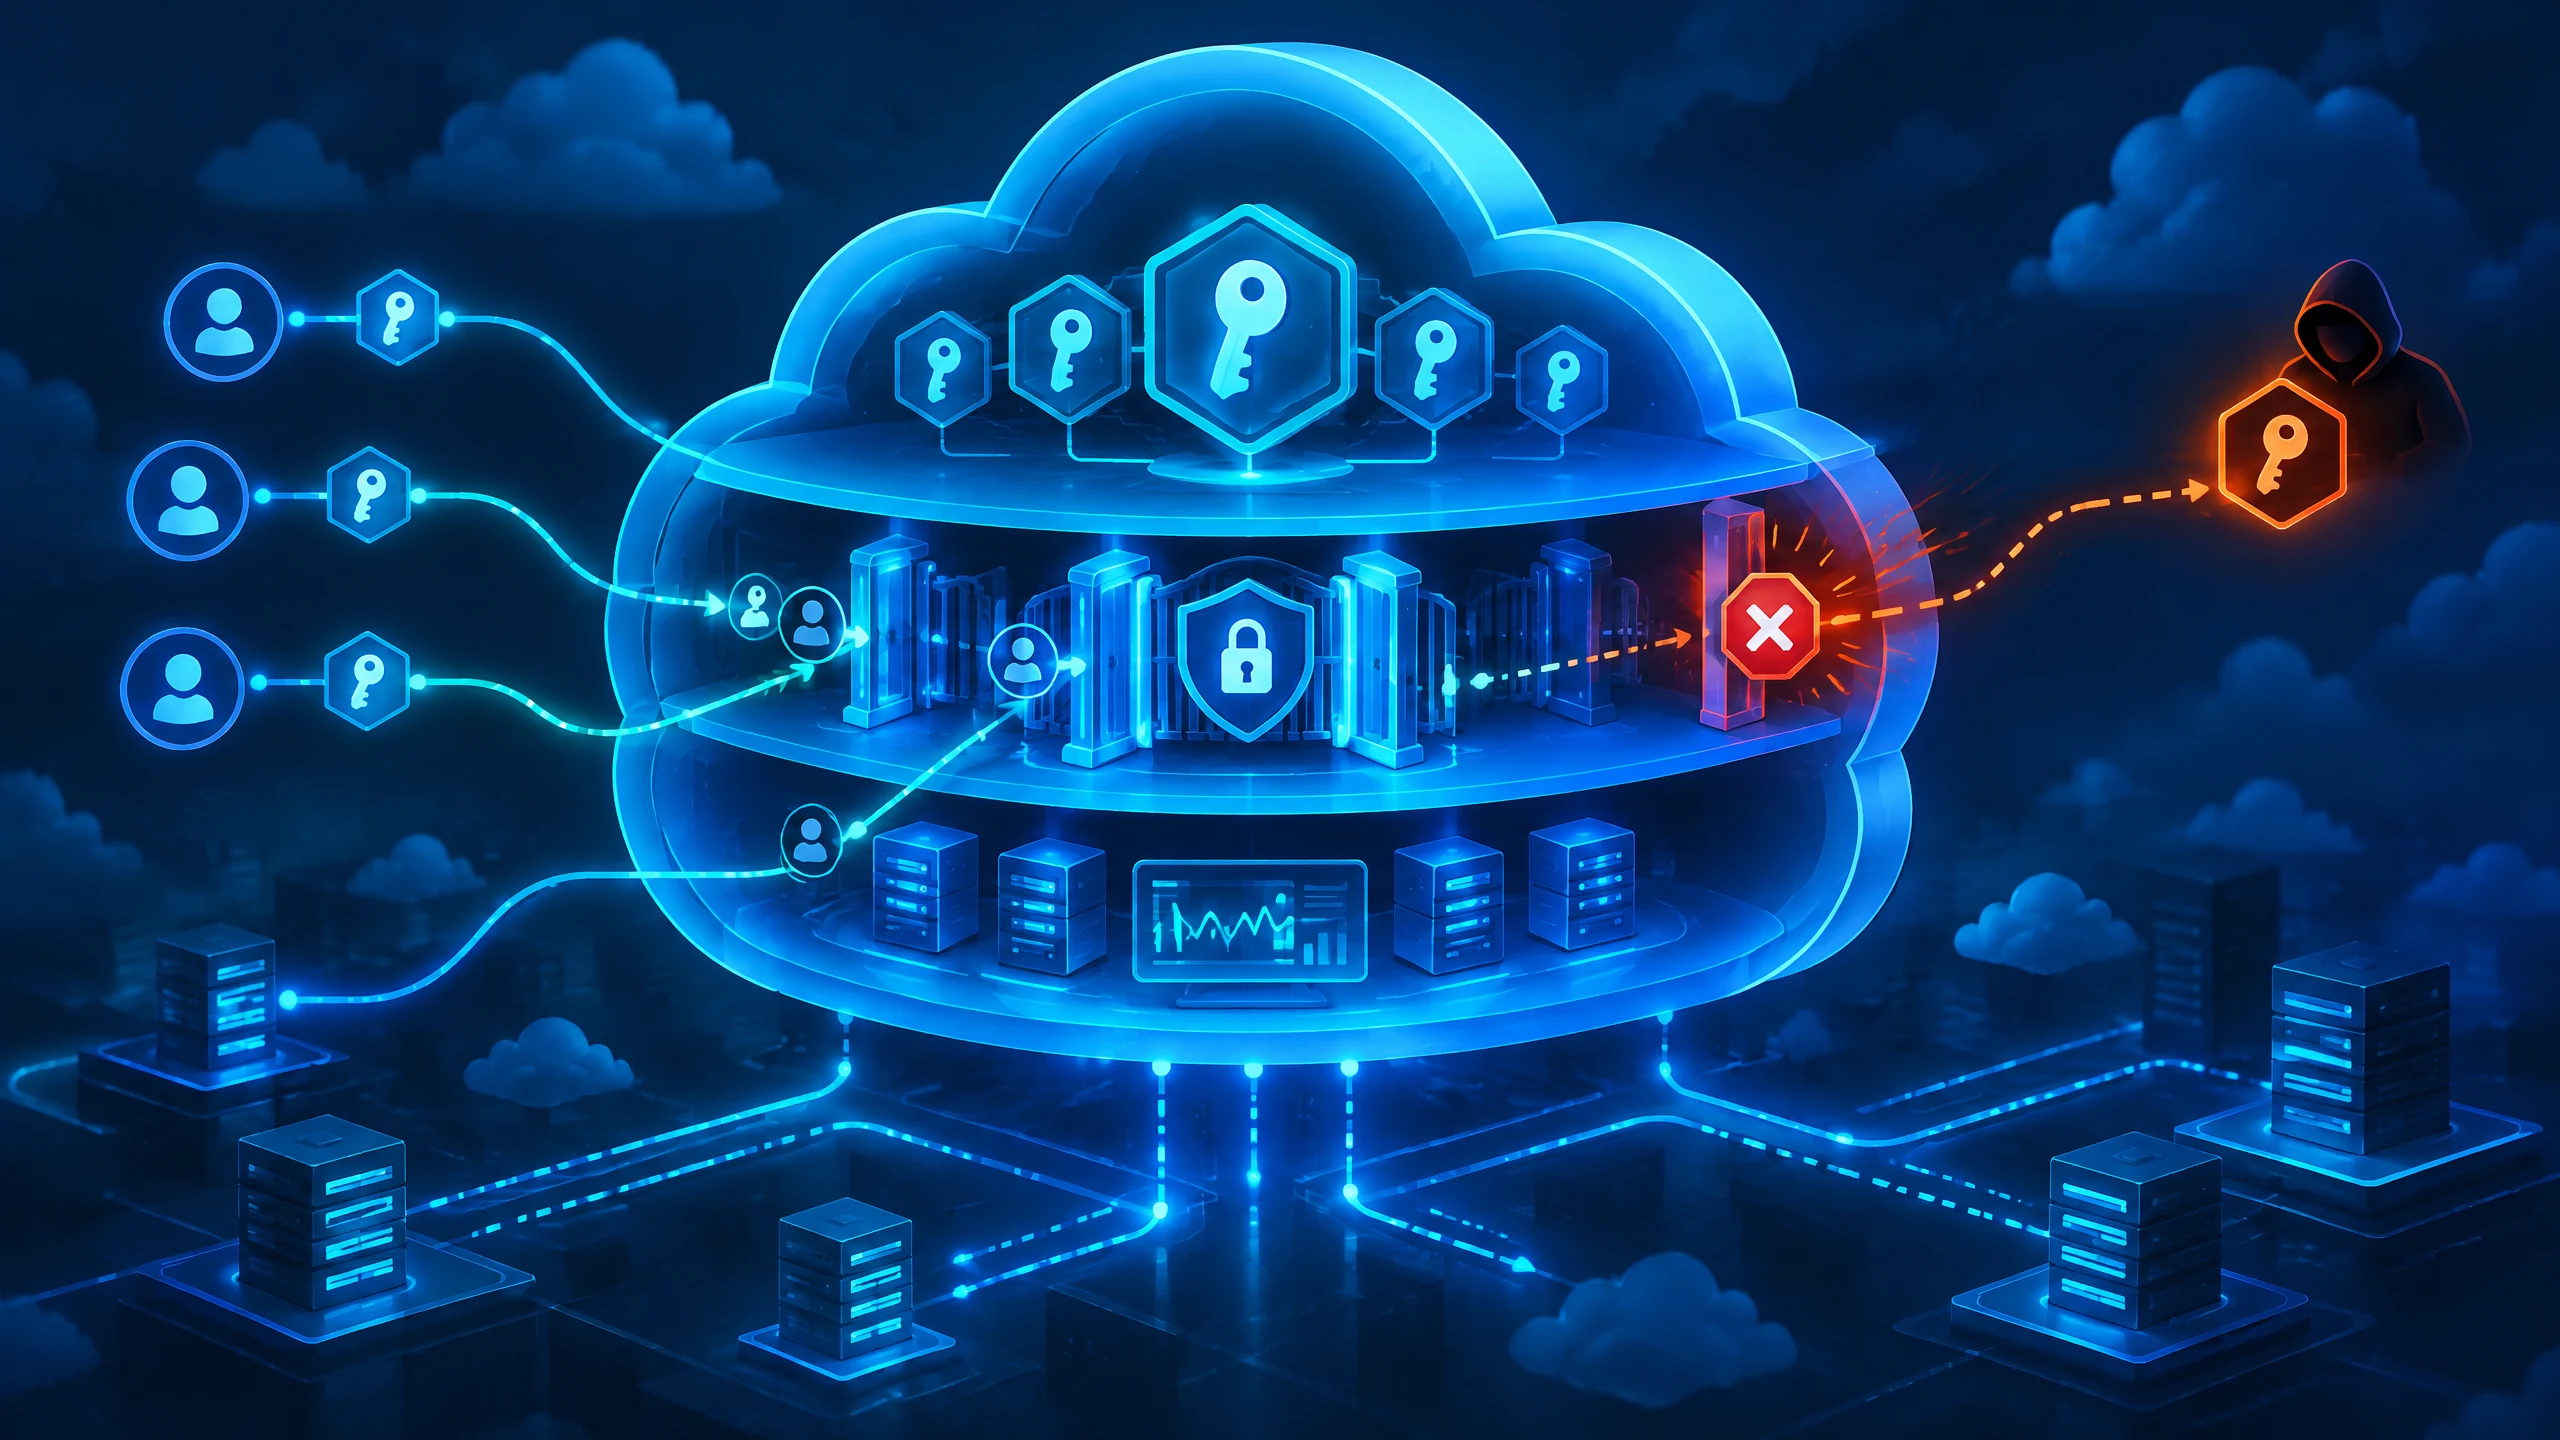
Cloud security misconfiguration** and identity abuse are closely connected defensive problems. A public resource, an exposed access token, an over-permissive role or weak separation between environments can create an opening. An abused identity can then turn that opening into unauthorised access, privilege escalation, persistence or data access. The relationship matters more than treating configuration and identity as separate checklists. This guide explains the connection in provider-neutral language. It focuses on what to review, what to monitor and how to respond without assuming that every cloud incident has the same cause. “Identity abuse” is a broad term here: it can include stolen credentials, compromised keys, forged tokens or assertions, token replay, MFA manipulation, rogue-device registration and excessive permissions. Not every identity event is a cloud incident, and not every cloud exposure proves identity abuse. The evidence base is practical rather than sensational. CISA and NIST address protection of cloud identity assertions, access tokens and cryptographic mechanisms in hybrid and multi-cloud environments. CERT-In discusses public accessibility, token protection, environment separation and least privilege. MeitY procurement guidance covers role separation, root and privileged IAM MFA, security-group review and monitoring. NSA/CISA guidance adds phishing-resistant MFA, secrets management, short-term credentials and safer administrative-key practices. > **Key Takeaways > - Review public access, identity permissions, environment separation and security-group rules together; each can change the impact of the others. > - Treat tokens, assertions, keys and secrets as high-value access material. Validate, protect, rotate and monitor them according to their role and exposure. > - Use least privilege, phishing-resistant MFA where possible, short-term credentials and controlled administration instead of shared or persistent administrator access. > - Preserve useful telemetry and investigate unusual token use, role changes, new accounts, device registration and unauthorised activity. > - Apply the customer-side controls required by your contract, sector and provider model; shared responsibility does not remove customer configuration duties.
What Cloud Security Misconfiguration Means
A cloud security misconfiguration is a setting or arrangement that leaves a resource, identity path or control weaker or more exposed than intended. Examples include an accidentally public service, an overly broad role, an unreviewed security-group rule, an exposed access token, weak separation between production and test environments, or incomplete logging. The common issue is not a particular provider; it is a gap between the intended security design and the running configuration.
CERT-In’s CIAD-2021-0004 advisory specifically warns that compromised or misconfigured cloud-based instances can contribute to data breaches and leaks. Its recommendations include checking whether cloud instances are publicly accessible, protecting AWS, Azure and GCP access tokens from exposure, separating production from test, staging and backup environments, applying least privilege and understanding the customer side of the shared-responsibility model. These are control priorities, not evidence of a universal incident rate.
Configuration also includes identity configuration. A role that can read more data than its job requires, a root or privileged account without strong additional protection, or a federation path that accepts an assertion without adequate validation can expand the blast radius of one mistake. CISA and NIST’s 15 September 2026 implementation recommendations put token and assertion validation, secrets management, scalable detection and Secure by Design in the same defensive conversation.
A useful review therefore asks two questions at once: **what can be reached, and which identity can reach it?** Map resources to accounts, roles, service identities, federation paths and machine credentials. Mark public exposure, administrative reach, data sensitivity and environment boundaries. This simple relationship map helps teams find dangerous combinations that a resource-only scan or identity-only review can miss.
How Cloud Security Misconfiguration Enables Identity Abuse
Identity abuse becomes more damaging when configuration gives an attacker an easy path from one credential or token to many resources. A stolen key may be limited if the associated role is narrow, short-lived and monitored. The same key can have a much wider effect when it belongs to a highly privileged identity, is valid for a long time, is shared across environments or is not covered by useful logs.
NSA/CISA describe identity-abuse paths that include credential theft, phishing, MFA-push manipulation, role or key creation, new cloud-account creation and federated-identity abuse. CISA’s cloud-identity guidance also discusses forged tokens, stolen credentials, token validation, secrets management and the detection difficulties created by limited telemetry or short log retention. These sources support a defensive conclusion: identity controls and configuration controls must be tested as a chain, not as isolated checkboxes.
The chain can begin with a public exposure, an accidentally committed secret, a compromised workstation or a social-engineering event. It may continue through a valid sign-in, token replay, a role change, a newly created key or a service-to-service request that appears technically legitimate. The goal of a defender is not to assume one fixed attack sequence, but to reduce the number of steps an abused identity can complete and to make unusual steps visible.
Use [identity attack paths and MFA bypass guidance](https://cyberoinfo.com/cybersecurity/identity-attacks) for the broader authentication context, and keep this page focused on the cloud configuration and identity-control intersection. For cloud teams, the practical questions are whether authentication is resistant to phishing where appropriate, whether authorisation is least-privilege, whether tokens and assertions are validated, and whether changes leave an investigation-quality record.
Cloud Security Misconfiguration Checklist
A reliable **cloud security misconfiguration checklist** should start with exposure and ownership. Inventory cloud accounts, subscriptions or projects, production and non-production environments, sensitive data stores, internet-facing services, identity providers, federated trust paths and service identities. For each item, record the business owner, intended access, administrative path, logging source and recovery contact. An inventory that has no owner is difficult to remediate safely.
Next, review access settings. Check public accessibility, storage and service permissions, network security groups, firewall rules, trust policies, role bindings and cross-account or cross-tenant relationships. Remove access that is not required, separate production from test, staging and backup environments, and require an explicit review for exceptions. CERT-In recommends these kinds of checks, while MeitY guidance calls for regular security-group review and monitoring for unauthorised activity.
Then inspect identity material. Protect access tokens, signing keys, assertions, API credentials and secrets from source code, tickets, logs and unapproved storage. Prefer short-term credentials where the platform supports them, avoid persistent root or administrative keys, and establish a documented rotation and revocation process. CISA/NIST emphasise token validation and secrets management; NSA/CISA recommend secure secrets management and avoiding root or administrative keys.
Finally, test the control boundary rather than only the setting. Ask whether a user can create a role, key, account, device or federation relationship outside the approved process. Confirm that privileged IAM accounts have MFA, that phishing-resistant methods are used where feasible, and that alerting covers unusual access, privilege changes, token use and unauthorised generation. Link this checklist with [phishing-resistant MFA and passkey guidance](https://cyberoinfo.com/cybersecurity/phishing-resistant-mfa) when choosing stronger authentication for administrators and sensitive workflows.
Detect and Respond to Cloud Identity Abuse
Detection starts with dependable telemetry. Collect identity-provider events, cloud control-plane activity, authentication outcomes, role and policy changes, key and token events, device registration, federation activity, network access and relevant application logs. CISA notes that limited telemetry or short retention can impede detection of forged tokens, compromised keys and unauthorised token generation, so retention and access to logs are part of the control design rather than an afterthought.
Prioritise signals that show a change in identity capability or normal use. Examples include a new privileged role, a newly created access key, a new cloud account, an unexpected federation change, unusual token validation outcomes, access from an unfamiliar context, a sudden change in service-to-service behaviour or a user who cannot explain a device registration. These signals need local baselines and careful triage; a single alert is not proof of compromise.
When an identity may be abused, contain the access path while preserving evidence. Depending on the situation, that can mean disabling or restricting the affected identity, revoking sessions or tokens, rotating exposed secrets, removing unauthorised roles or keys, blocking a suspicious federation relationship and protecting critical resources from further change. Coordinate with the identity, cloud, application and incident-response owners so that containment does not destroy the evidence needed to understand scope.
After containment, compare intended configuration with observed changes, review access to sensitive resources, check for persistence and validate recovery credentials. Document the initial exposure, the identity path, the permissions used, the logs available and the controls that need improvement. For related application-to-application access, the [API security guide](https://cyberoinfo.com/cybersecurity/api-security) provides a complementary control lens without replacing cloud IAM review.
India Controls and Shared Responsibility
For Indian organisations, the applicable contract, sector obligations and procurement terms determine which requirements apply. MeitY’s Guidelines for Procurement of Cloud Services call for role-separated IAM and least privilege, proper administration of root and IAM users, MFA for root and privileged IAM accounts, regular security-group review, monitoring for unauthorised activity and two-factor authentication for relevant IaaS access. Treat these as concrete control points to map against the organisation’s cloud design, while checking the current agreement and applicable rules before making a compliance claim.
CERT-In’s cloud advisory is useful for operational review: check public access, protect cloud access tokens, separate production from test, staging and backup, apply least privilege and understand the customer side of shared responsibility. The provider may operate the underlying service, but the customer can still control identities, permissions, data access, network rules, secrets, workloads and logging choices. The exact boundary differs by service model and contract.
A practical India-focused review should assign named owners for root and privileged IAM accounts, confirm MFA and recovery procedures, review security groups on a recurring schedule, retain investigation-quality logs and test the response to exposed credentials. It should also distinguish guidance from legal advice. The evidence file supports these controls; it does not support a claim that every Indian company has the same obligations or that one checklist guarantees compliance.
Teams that need a broader organisational view can connect this page with [data-breach response planning](https://cyberoinfo.com/cybersecurity/data-breach-response) and document how cloud identity events fit into escalation, evidence preservation and notification decisions. The purpose is continuity: configuration review, identity monitoring and incident response should reinforce one another rather than operate as separate programmes.
FAQ: Cloud Security Misconfiguration and Identity Abuse
Can a cloud security misconfiguration cause identity abuse?** It can create conditions that make identity abuse easier or more damaging, such as exposing a credential, granting an overly broad role or leaving a federation path weakly controlled. It does not prove that an identity was abused. Confirm the actual access path through configuration review, identity events, token or key activity and application logs.
What should be checked first?** Start with public exposure, privileged identities, access tokens and secrets, environment separation, security-group rules and logging coverage. Then check whether MFA protects root and privileged accounts, whether permissions are least privilege, whether credentials are short-lived where possible and whether unusual role, key, account or device changes are visible.
Does shared responsibility mean the cloud provider handles the problem?** No. The provider and customer have different responsibilities, and the boundary depends on the service model. Customer-controlled identities, permissions, workloads, secrets, data access and many network settings still require customer governance. Review the provider’s responsibility description alongside the contract and your own configuration evidence.
Limitations
- Evidence and guidance can change; verify current advisories and organisational applicability before acting.
Evidence sources
- cisa.gov — CISA/NIST final implementation recommendations for agencies and cloud service providers, 15 September 2026
- cisa.gov — CISA, Securing Core Cloud Identity Infrastructure, 15 July 2025; revised 15 September 2026
- trends.google.com — Google Trends comparison for India: cloud security misconfiguration, cloud IAM, identity abuse
- cert-in.org.in — CERT-In Advisory CIAD-2021-0004, Preventing Data Breaches / Data leaks
- meity.gov.in — MeitY Guidelines for Procurement of Cloud Services
- media.defense.gov — NSA/CISA, Use Secure Cloud Identity and Access Management Practices, March 2024