Network Security
Network Segmentation, Explained Clearly
How thoughtful boundaries can slow lateral movement and protect high-value systems without blocking useful work.
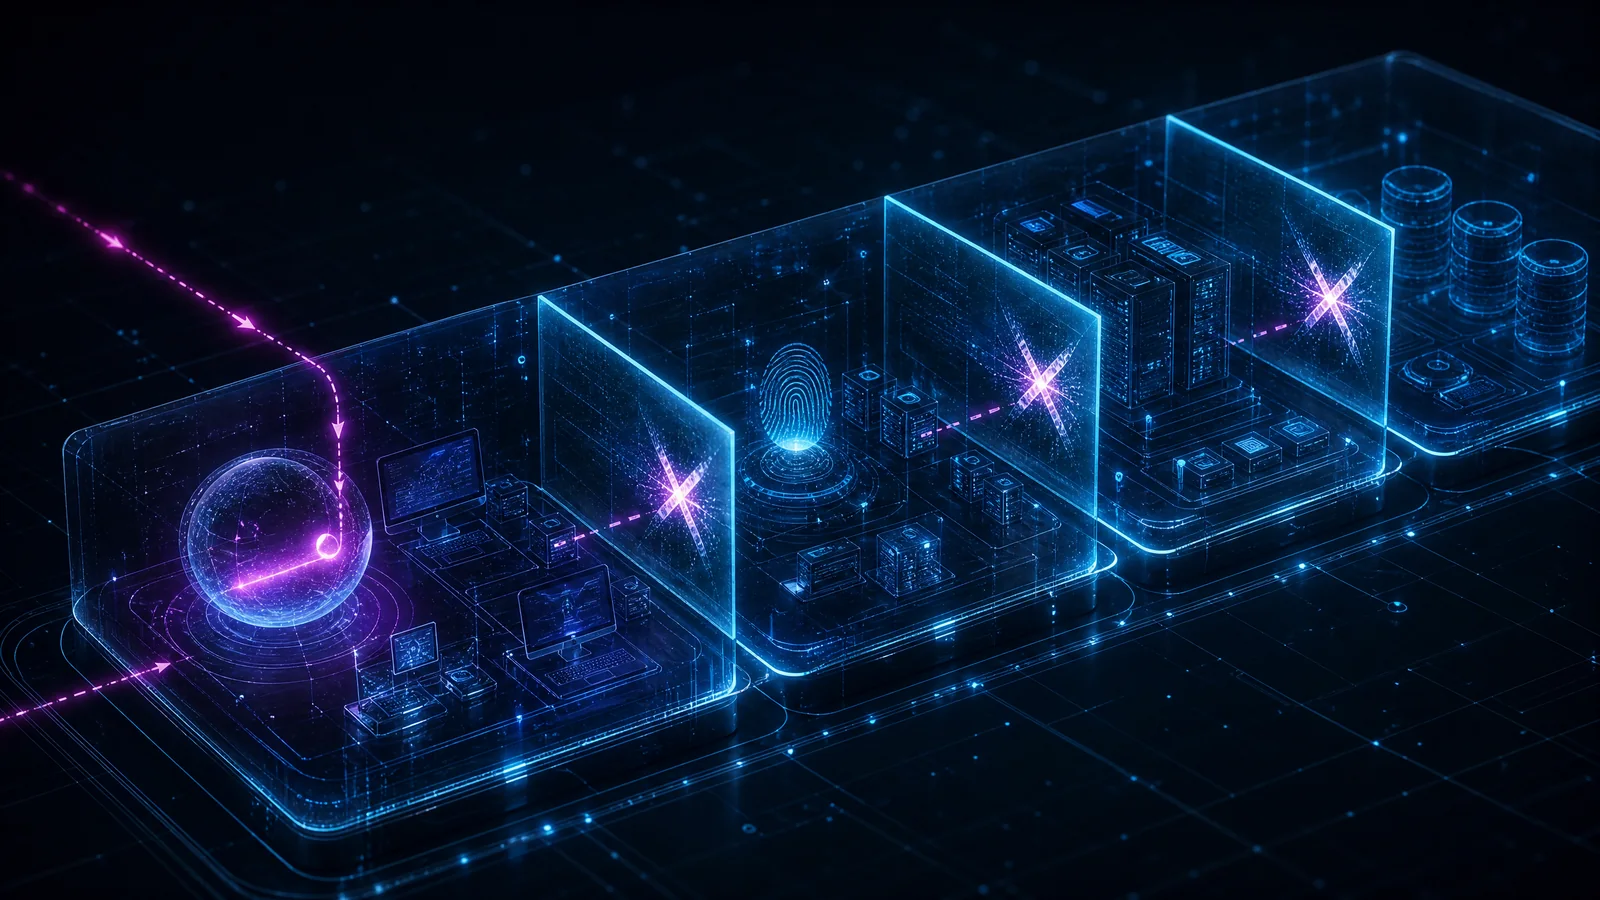
A flat network turns one compromised account, workstation, or exposed service into a possible route toward systems that have no operational reason to trust it. Segmentation replaces that implicit trust with deliberately controlled paths. It groups assets by function and sensitivity, then uses firewalls, access-control lists, identity-aware policy, and monitoring to decide which communications are allowed across each boundary. The objective is not to create as many network zones as possible. It is to make every permitted connection understandable, necessary, observable, and revocable. This guide explains the architectural decisions behind effective segmentation, the difference between VLAN separation and enforced security boundaries, and the ways attackers exploit overly broad east-west access. It also shows how teams can inventory critical flows, choose practical trust zones, test default-deny rules, detect boundary violations, and phase changes without interrupting essential services. The result is a usable model for reducing lateral movement and limiting incident impact while recognizing that segmentation must be maintained as applications, identities, devices, and business dependencies change.
What is network segmentation?
At its core, network segmentation is the practice of splitting a computer network into smaller, isolated sub-networks. Each of these segments acts as its own small network, with specific rules governing how traffic can flow in and out. The primary goal is to improve security and performance by ensuring that users and devices only have access to the resources necessary for their specific functions.
Think of it like the bulkheads in a submarine. If one section is breached and begins to flood, the bulkheads can be sealed to prevent the water from sinking the entire vessel. Similarly, if an attacker compromises a single workstation in a segmented network, they are restricted to that specific segment, preventing them from easily moving laterally to access critical servers or sensitive databases.
Why it matters
In modern IT environments, the traditional perimeter defense model is no longer sufficient. Attackers frequently bypass edge firewalls through phishing, credential theft, or exploiting vulnerable public-facing applications. Once inside a flat network, where everything can communicate with everything else, the attacker has unrestricted freedom to explore, escalate privileges, and exfiltrate data.
Segmentation changes this dynamic. By establishing internal boundaries, organizations force attackers to work harder to reach their objectives. Each boundary crossed requires additional exploits or compromised credentials, increasing the likelihood that the attacker's activities will generate noise and be detected by security monitoring tools before significant damage occurs.
Furthermore, segmentation is critical for compliance with many regulatory frameworks. Standards such as the Payment Card Industry Data Security Standard (PCI DSS) require organizations to isolate systems that process credit card data from the rest of the corporate network. Proper segmentation not only enhances security but also drastically reduces the scope and cost of compliance audits.
Threat models
Network segmentation primarily addresses the threat of lateral movement. Advanced Persistent Threats (APTs) and ransomware operators rarely land directly on their ultimate target. Instead, they gain an initial foothold on a low-value asset and then pivot through the network, searching for domain controllers, sensitive data repositories, or backup systems.
Ransomware, in particular, thrives in flat networks. Once a single machine is infected, the malware can rapidly propagate to encrypt thousands of endpoints and servers. Segmentation disrupts this kill chain. If a ransomware infection occurs in a segregated guest Wi-Fi network or a specific departmental VLAN, the infection is contained to that area, sparing the organization's core operations and critical data.
Impact
The impact of implementing network segmentation is profound. It transforms a fragile, single-point-of-failure environment into a resilient architecture. Beyond security, segmentation can also improve network performance by localizing traffic and reducing broadcast storms, ensuring that critical applications receive the necessary bandwidth.
However, the operational impact must also be considered. Managing a segmented network requires careful planning, accurate asset inventory, and a deep understanding of application communication requirements. Misconfigured segmentation can inadvertently block legitimate business traffic, causing operational disruptions and frustrating users.
Detection
Segmentation significantly enhances an organization's detection capabilities. By routing traffic between segments through internal firewalls or intrusion detection systems (IDS), security teams gain visibility into internal network flows. This is crucial because internal traffic often constitutes the majority of network activity and is frequently blind spot in flat networks.
Security analysts can establish baselines for normal communication between specific segments. For example, the HR subnet should regularly communicate with the payroll server, but the engineering subnet should not. When anomalous traffic attempts to cross these boundaries, it serves as a high-fidelity alert, indicating potential lateral movement or a misconfiguration.
Response
When a segmentation violation or lateral movement is detected, the response should involve immediately investigating the source and destination of the traffic. If the activity is deemed malicious, the affected segment can be further isolated or disconnected from the rest of the network to contain the threat.
Incident response teams should leverage the existing segmentation architecture to quickly quarantine compromised assets and analyze the traffic patterns to understand the attacker's objectives and methods.
Prevention and architecture
Start with accurate ownership, narrow access, useful logging, secure defaults, and a rehearsed response. Protection improves when teams know which assets matter and who can make urgent decisions. Implement a strict, default-deny ACL strategy to control traffic between segments.
Modern architectures increasingly rely on microsegmentation, which applies security policies at the individual workload level rather than just at the network subnet level. This approach, often part of a Zero Trust architecture, provides granular control and adapts to dynamic environments like cloud infrastructure.
Implementing segmentation requires a phased approach. Organizations should begin by identifying and isolating their most critical assets, often referred to as the 'crown jewels.' This might involve creating a dedicated segment for databases containing personally identifiable information (PII) or financial records. Subsequent phases can involve segmenting user workstations by department or function.
Network Access Control (NAC) solutions can complement segmentation by dynamically assigning devices to specific segments based on their identity, posture, and authorization level. This ensures that only trusted and compliant devices can access sensitive areas of the network, further reducing the attack surface.
Regular audits and reviews of segmentation policies are essential to maintain their effectiveness. As business requirements evolve and new applications are deployed, segmentation rules must be updated to accommodate these changes without introducing unnecessary risk. Automation and orchestration tools can streamline this process and ensure consistent policy enforcement across the entire network.
Worked example
Consider a mid-sized healthcare provider that recently suffered a data breach due to a flat network architecture. An attacker gained initial access by phishing a receptionist, then moved laterally to access patient records stored on a central database server.
To prevent future incidents, the organization implemented a segmented network architecture. They created separate segments for guest Wi-Fi, administrative staff, clinical devices (e.g., MRI machines, patient monitors), and the core data center hosting electronic health records (EHR).
Strict access control lists (ACLs) were applied between these segments. For example, clinical devices were only allowed to communicate with specific servers in the data center required for their operation, and administrative staff were blocked from accessing the clinical device segment entirely.
When a subsequent phishing attack compromised a billing clerk's workstation, the attacker was unable to pivot to the EHR database because the segmentation rules blocked that traffic. The security team was immediately alerted to the blocked connection attempt, allowing them to isolate the compromised workstation and remediate the threat before any sensitive data was exposed.
Decision checklist
- Identify and inventory all critical assets and sensitive data repositories.
- Map existing network data flows and communication requirements.
- Define logical segments based on business function, data sensitivity, and risk profile.
- Implement firewalls, VLANs, and ACLs to enforce boundaries between segments.
- Apply a default-deny policy for traffic crossing segment boundaries.
- Ensure administrative interfaces are only accessible from dedicated, secure management segments.
- Monitor and log all traffic between segments for anomalous activity.
- Regularly review and update segmentation policies to align with business changes.
- Consider microsegmentation for granular control in cloud and virtualized environments.
- Test the effectiveness of segmentation controls through penetration testing and red team exercises.
Limitations
- Network segmentation can increase network complexity and administrative overhead.
- Overly restrictive segmentation policies can disrupt legitimate business operations if not carefully planned.
- Segmentation primarily addresses network-level threats and must be combined with endpoint security and identity management for comprehensive protection.
- Legacy applications may struggle to operate in highly segmented environments.
- Without continuous monitoring and regular audits, segmentation rules can become stale and ineffective over time, leading to a false sense of security.
Evidence sources
- NSA & CISA — Implement Network Segmentation and Encryption in Cloud Environments
- CISA — Enhanced Visibility and Hardening Guidance for Communications Infrastructure
- NIST — NIST SP 800-215: Guide to a Secure Enterprise Network Landscape
- NIST — Zero Trust Architecture (ZTA)