Cloud Security
Vishing, Token Replay, and SaaS Extortion: Defending the PREY-0058 Pattern
How help-desk vishing, adversary-in-the-middle credential capture, and residential-proxy session replay can lead to SaaS data theft and extortion without endpoint malware.
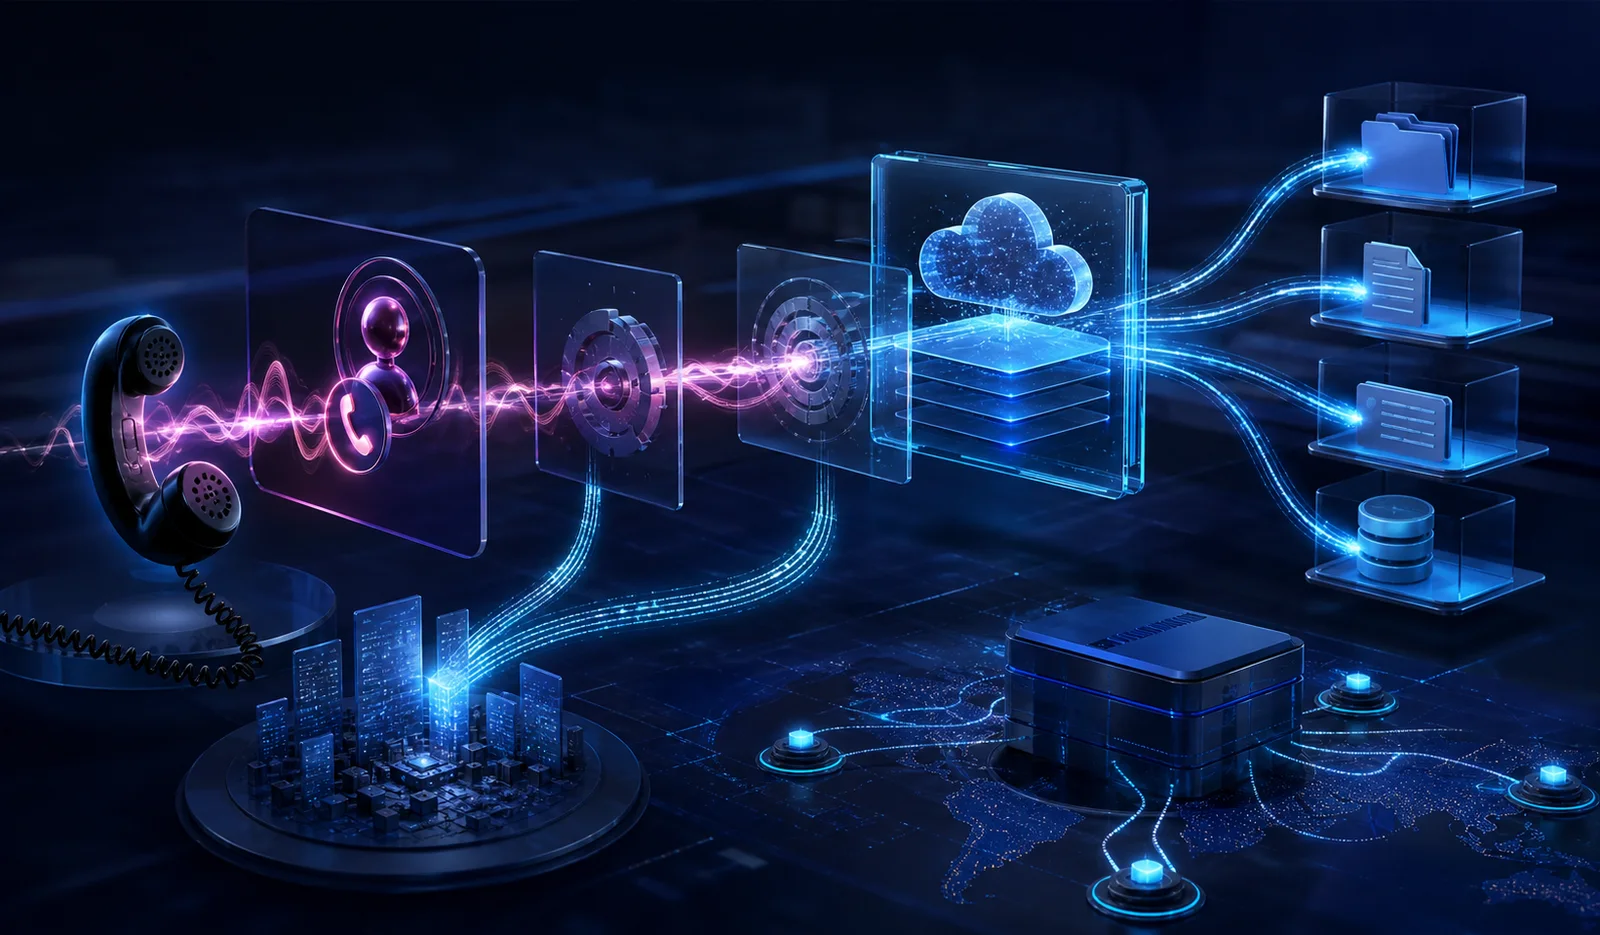
The PREY-0058 reporting describes a cloud-identity intrusion pattern: help-desk vishing leads victims to attacker-controlled authentication flows, captured credentials and MFA approvals are used to replay sessions through residential proxies, and operators collect SaaS data. The report qualifies actor and extortion-brand relationships rather than treating the labels as a single confirmed organization.
The identity-led attack path
Arctic Wolf tracked a cluster targeting U.S. directors, vice presidents, and other executives through help-desk vishing and victim-specific authentication-themed domains. Operator-controlled adversary-in-the-middle flows captured credentials and MFA approvals, followed by session replay through residential proxies intended to resemble a victim’s location and network context.
The observed post-compromise activity included enumeration of Microsoft 365 and Entra ID resources and collection from SharePoint, OneDrive, Exchange, and Box. Arctic Wolf reported no endpoint-malware deployment or network-based lateral movement in this cluster.
Controls that interrupt token replay
Require independent verification for unexpected help-desk calls, and prohibit cold-call MFA or passkey enrollment. Use phishing-resistant FIDO2 or passkey authentication together with managed-device requirements, Conditional Access, short session lifetimes, continuous access evaluation, and least-privilege SharePoint access.
Monitor for residential-proxy token replay, unusual My Signins, My Profile, or My Apps activity, rare SharePoint searches, high-volume FileAccessed, FileDownloaded, or MailItemsAccessed events, scripting user agents, and newly registered passkey- or MFA-themed look-alike domains.
Avoid overclaiming attribution
PREY-0058, UNC6671, Cinder, Pink, BlackFile, Redact, Helix, and Falcon were described as overlapping tradecraft, infrastructure, victim, or extortion-brand labels. Shared services, affiliates, splinter groups, and outsourced extortion can produce overlapping evidence, so defensive decisions should be based on observed behavior rather than assumed actor identity.