Ransomware
How Ransomware Attacks Modern Businesses
Follow the attack path from an initial foothold to enterprise-wide disruption—and identify the decisions that can interrupt it.
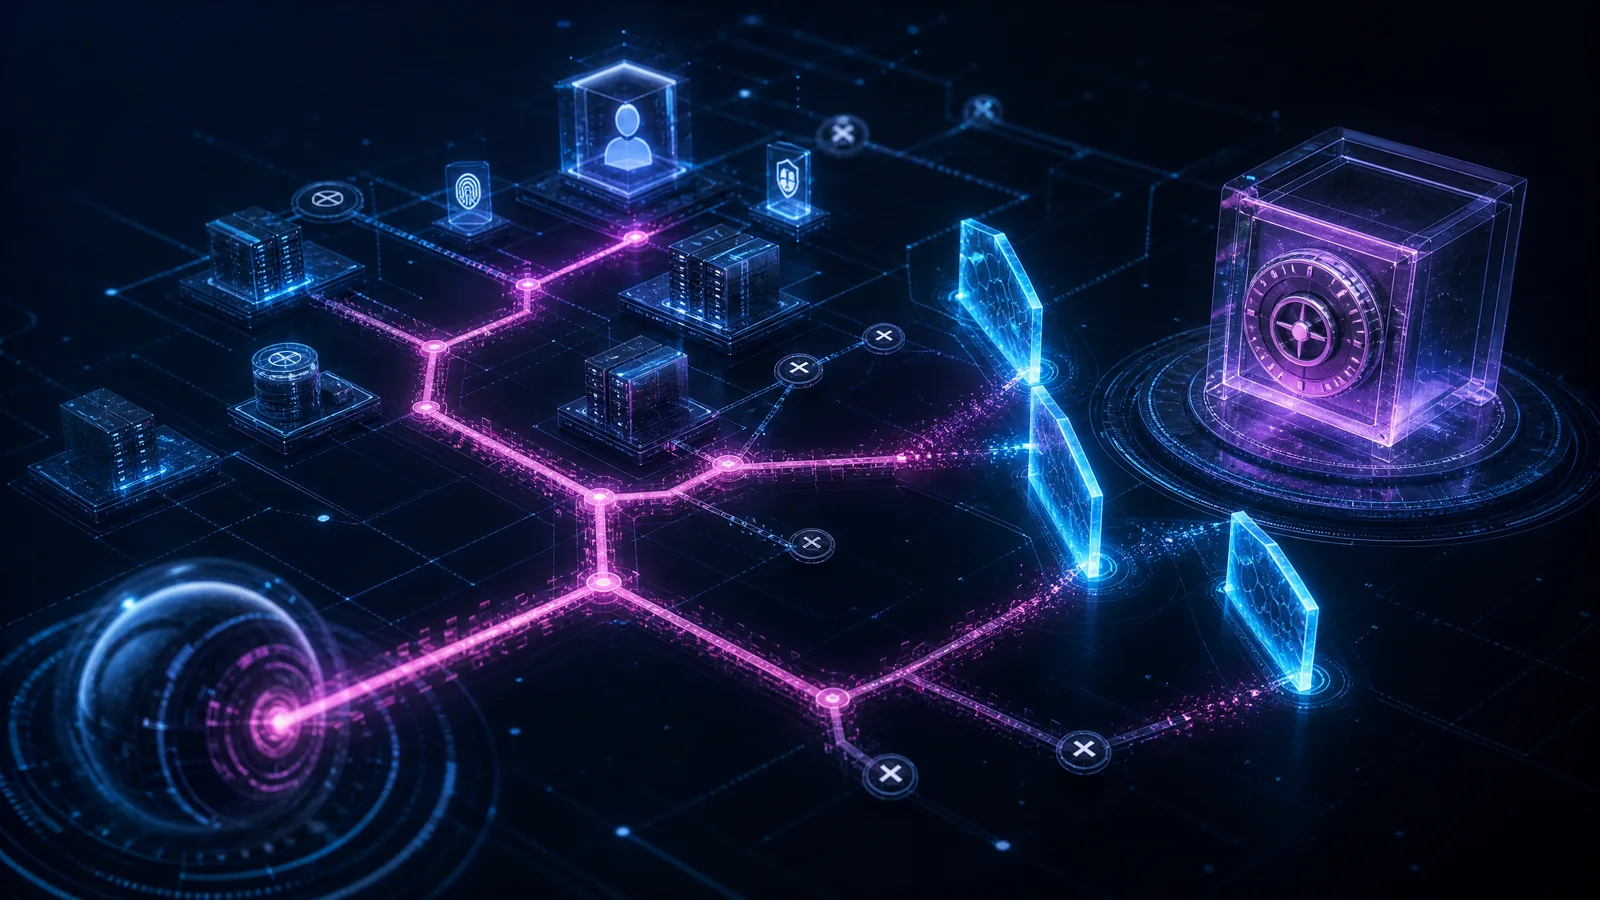
Ransomware is best understood as a sequence of access, discovery, control, and pressure rather than a single encryption event. Modern ransomware operations are highly structured, often involving specialized affiliates who purchase access, explore the network, escalate privileges, and strategically position themselves for maximum impact. By the time encryption occurs, the attackers have typically already compromised critical infrastructure, disabled security controls, and exfiltrated sensitive data to use for double extortion. Understanding this lifecycle is critical for defense, as it provides multiple opportunities to detect and disrupt the attack before irreversible damage occurs. This article explores the stages of a ransomware attack, the observable signals at each phase, and the architectural and procedural controls necessary to build resilience. Furthermore, the ecosystem has evolved into a Ransomware-as-a-Service (RaaS) model, where core developers maintain the malicious infrastructure and encryption tools, while independent affiliates conduct the actual network intrusions. This specialization has dramatically increased the volume and sophistication of attacks, as affiliates can focus entirely on breaching networks using advanced techniques like exploiting zero-day vulnerabilities, purchasing stolen session cookies from initial access brokers, or executing sophisticated social engineering campaigns against help desks. The shift to double and triple extortion—where attackers not only encrypt data but also threaten to leak sensitive information publicly and harass the victim's clients or partners—has fundamentally altered the risk calculus for organizations, making preventative measures and rapid detection more critical than ever before. Security teams must adapt by adopting an assume-breach mentality, implementing zero-trust architecture principles, and ensuring continuous monitoring of all identities and endpoints across the hybrid enterprise environment.
Executive Answer
Ransomware is an extortion operation in which attackers disrupt access to systems or data and demand payment. Many operations also steal information to increase pressure.
Rather than a sudden, unpredictable event, a ransomware attack is a process. Attackers establish a foothold, map the environment, acquire administrative credentials, and systematically dismantle defenses before executing the final encryption payload.
The modern ransomware landscape is characterized by its professionalization. Threat actors operate like legitimate businesses, complete with human resources departments, customer support for victims negotiating ransom payments, and operator-partner models that distribute the workload of compromising networks. This industrialization of cybercrime means that attacks are no longer random occurrences but targeted campaigns executed by skilled adversaries with significant resources.
Understanding this structure is essential for defense. By recognizing that ransomware is a multi-stage operation, organizations can deploy controls at various points in the attack lifecycle. Disruption at the initial access, lateral movement, or data exfiltration stages can prevent the final, devastating encryption event, thereby transforming a potentially catastrophic incident into a manageable security event.
Scope and Threat Model
The threat model for modern ransomware extends beyond simple malware execution. It encompasses initial access brokers (IABs) who compromise edge devices or steal credentials, and affiliates who perform the hands-on-keyboard intrusion.
Organizations must defend against phishing, exploitation of public-facing applications (like VPNs), and the abuse of valid accounts. The goal of the attacker is to gain sufficient control over the environment to force a ransom payment.
The threat model must also account for the increasing targeting of supply chains and managed service providers (MSPs). By compromising a single entity that has trusted access to multiple downstream clients, attackers can exponentially increase their impact and potential payout. This requires organizations to rigorously evaluate the security posture of their third-party vendors and enforce strict access controls on any external connections.
Additionally, the proliferation of remote work has expanded the attack surface, making endpoints located outside the traditional corporate perimeter prime targets. Attackers frequently exploit vulnerabilities in unpatched virtual private networks (VPNs), remote desktop protocol (RDP) instances, and other remote access solutions to gain their initial foothold, highlighting the need for robust endpoint security and continuous vulnerability management.
How the Issue Works
Encryption is usually a late stage. Operators first seek access, learn the environment, expand privilege, identify critical services, weaken recovery options, and position themselves for maximum impact.
Attackers often use legitimate administrative tools (Living off the Land techniques) to move laterally and evade detection. They target domain controllers, virtualization infrastructure, and backup systems to ensure the victim cannot easily recover.
Once inside, attackers meticulously map the network topology, identifying key assets such as domain controllers, file servers, and databases. They actively seek out privileged accounts, often using tools like BloodHound to identify the shortest path to Domain Admin privileges. This reconnaissance phase is critical for the attackers to understand the environment and plan their subsequent actions.
Before deploying the ransomware payload, attackers systematically disable or bypass security controls. They may tamper with endpoint detection and response (EDR) agents, delete volume shadow copies, and compromise backup servers to ensure that the victim cannot restore their systems without paying the ransom. This deliberate degradation of the organization's resilience is a hallmark of sophisticated ransomware operations.
Exposure or Indicators
Observable signals of a ransomware intrusion often precede the encryption event by days or weeks. These include unusual remote access logins, the execution of network scanning tools, and the sudden creation of new administrative accounts.
Other indicators include the presence of data exfiltration tools (like Rclone), unexpected modifications to group policies, and the disabling of endpoint detection and response (EDR) software.
Behavioral indicators are often the most reliable way to detect a ransomware intrusion before encryption occurs. These include the execution of dual-use tools—legitimate administrative utilities like PowerShell, PsExec, or Windows Management Instrumentation (WMI)—in unusual contexts or by unexpected users. Monitoring for the anomalous use of these tools is crucial for identifying attackers living off the land.
Network-level indicators also provide valuable early warning signs. Unusual outbound traffic patterns, particularly large volumes of data being transferred to known cloud storage providers or unfamiliar IP addresses, can indicate the data exfiltration phase. Additionally, the sudden appearance of new, unapproved remote access tools (such as AnyDesk or TeamViewer) on critical servers is a strong indicator of unauthorized access and potential impending ransomware deployment.
Impact
Operational interruption, data exposure, recovery costs, legal obligations, and loss of trust can continue long after systems are restored.
The financial impact includes not only the potential ransom payment but also lost revenue, forensic investigation fees, system rebuilding costs, and potential regulatory fines for data breaches.
The impact of a ransomware attack extends far beyond the immediate technical disruption. Organizations often face significant reputational damage, as the public disclosure of a breach can erode customer trust and lead to a loss of business. In highly regulated industries, such as healthcare or finance, the exposure of sensitive data can result in severe regulatory penalties and class-action lawsuits.
Furthermore, the operational downtime caused by ransomware can have cascading effects on supply chains and critical infrastructure. For manufacturing companies, halted production lines can result in massive financial losses. For healthcare providers, the inability to access patient records or operate medical equipment can directly impact patient safety, underscoring the critical nature of robust ransomware defenses in these sectors.
Detection
Effective detection requires monitoring for behavioral anomalies rather than just known malware signatures. This includes alerting on impossible travel logins, unusual lateral movement patterns, and the unexpected use of administrative tools.
Security teams should also monitor for large-scale data transfers to unknown external IP addresses, which often indicates the exfiltration phase of a double-extortion attack.
To effectively detect ransomware activity, organizations must implement comprehensive logging and monitoring across their entire IT environment. This includes centralizing logs from endpoints, network devices, identity providers, and cloud services into a Security Information and Event Management (SIEM) system. Correlating these diverse data sources enables security teams to identify complex attack patterns that might be missed by analyzing individual alerts in isolation.
Threat hunting is another essential component of a proactive detection strategy. Rather than waiting for alerts to trigger, security analysts should actively search the environment for indicators of compromise (IoCs) and anomalous behaviors associated with known ransomware groups. This proactive approach can uncover hidden intrusions that have evaded automated detection mechanisms, allowing the organization to respond before the attack escalates.
Response
Incident response for ransomware must be rapid and coordinated. The immediate priority is containment—isolating compromised segments to prevent the spread of the infection.
Organizations should not immediately reboot affected systems, as this can destroy volatile forensic evidence in memory. Instead, they should follow a predefined incident response playbook that includes legal and communication strategies.
A critical aspect of incident response is effective communication. Organizations must have a predefined communication plan that outlines how to inform internal stakeholders, external customers, regulatory bodies, and law enforcement agencies about the incident. Transparent and timely communication is essential for managing the organization's reputation and complying with legal obligations during a crisis.
Prevention and Architecture
Reduce standing privilege, segment critical systems, monitor identity changes, protect backups from routine administrative access, and rehearse containment decisions before an emergency.
Implementing multi-factor authentication (MFA) on all remote access and administrative accounts is critical. Backups must be immutable and isolated from the primary network to ensure they cannot be encrypted or deleted by the attackers.
Implementing a Zero Trust architecture is fundamental to preventing ransomware attacks. This approach assumes that the network is already compromised and requires strict identity verification and device health checks for every access request, regardless of the user's location. By enforcing the principle of least privilege and micro-segmenting the network, organizations can significantly limit the lateral movement capabilities of attackers.
Decision checklist
- Have we implemented MFA for all remote access and administrative accounts?
- Are our backups immutable and logically separated from the primary network?
- Do we have an established and tested incident response plan for ransomware?
- Is our EDR solution deployed across all endpoints and actively monitored?
- Have we segmented our network to limit lateral movement?
- Do we conduct regular vulnerability scanning and patching of internet-facing systems?
- Are we monitoring for unusual data exfiltration activity?
Limitations
- This article provides general guidance and may not cover all specific ransomware variants or novel attack techniques.
- The effectiveness of the recommended controls depends on their proper implementation and ongoing maintenance within the specific organizational context.
- The threat landscape evolves rapidly, and this guidance cannot anticipate undiscovered initial access vectors or zero-day exploits used by advanced ransomware operators.
Evidence sources
- Cybersecurity and Infrastructure Security Agency (CISA) — StopRansomware Guide
- MITRE ATT&CK — Data Encrypted for Impact, Technique T1486
- National Institute of Standards and Technology (NIST) — IR 8374 Rev. 1, Ransomware Risk Management
- Onapsis — Understanding & Defending Against Ransomware Attacks