Security Operations
Security Operations in 2026: SIEM, XDR, SOAR, and the AI-Augmented SOC
A practical 2026 guide to security operations, explaining how SIEM, XDR, SOAR, agentic SOC workflows, threat hunting, and human approval fit together.
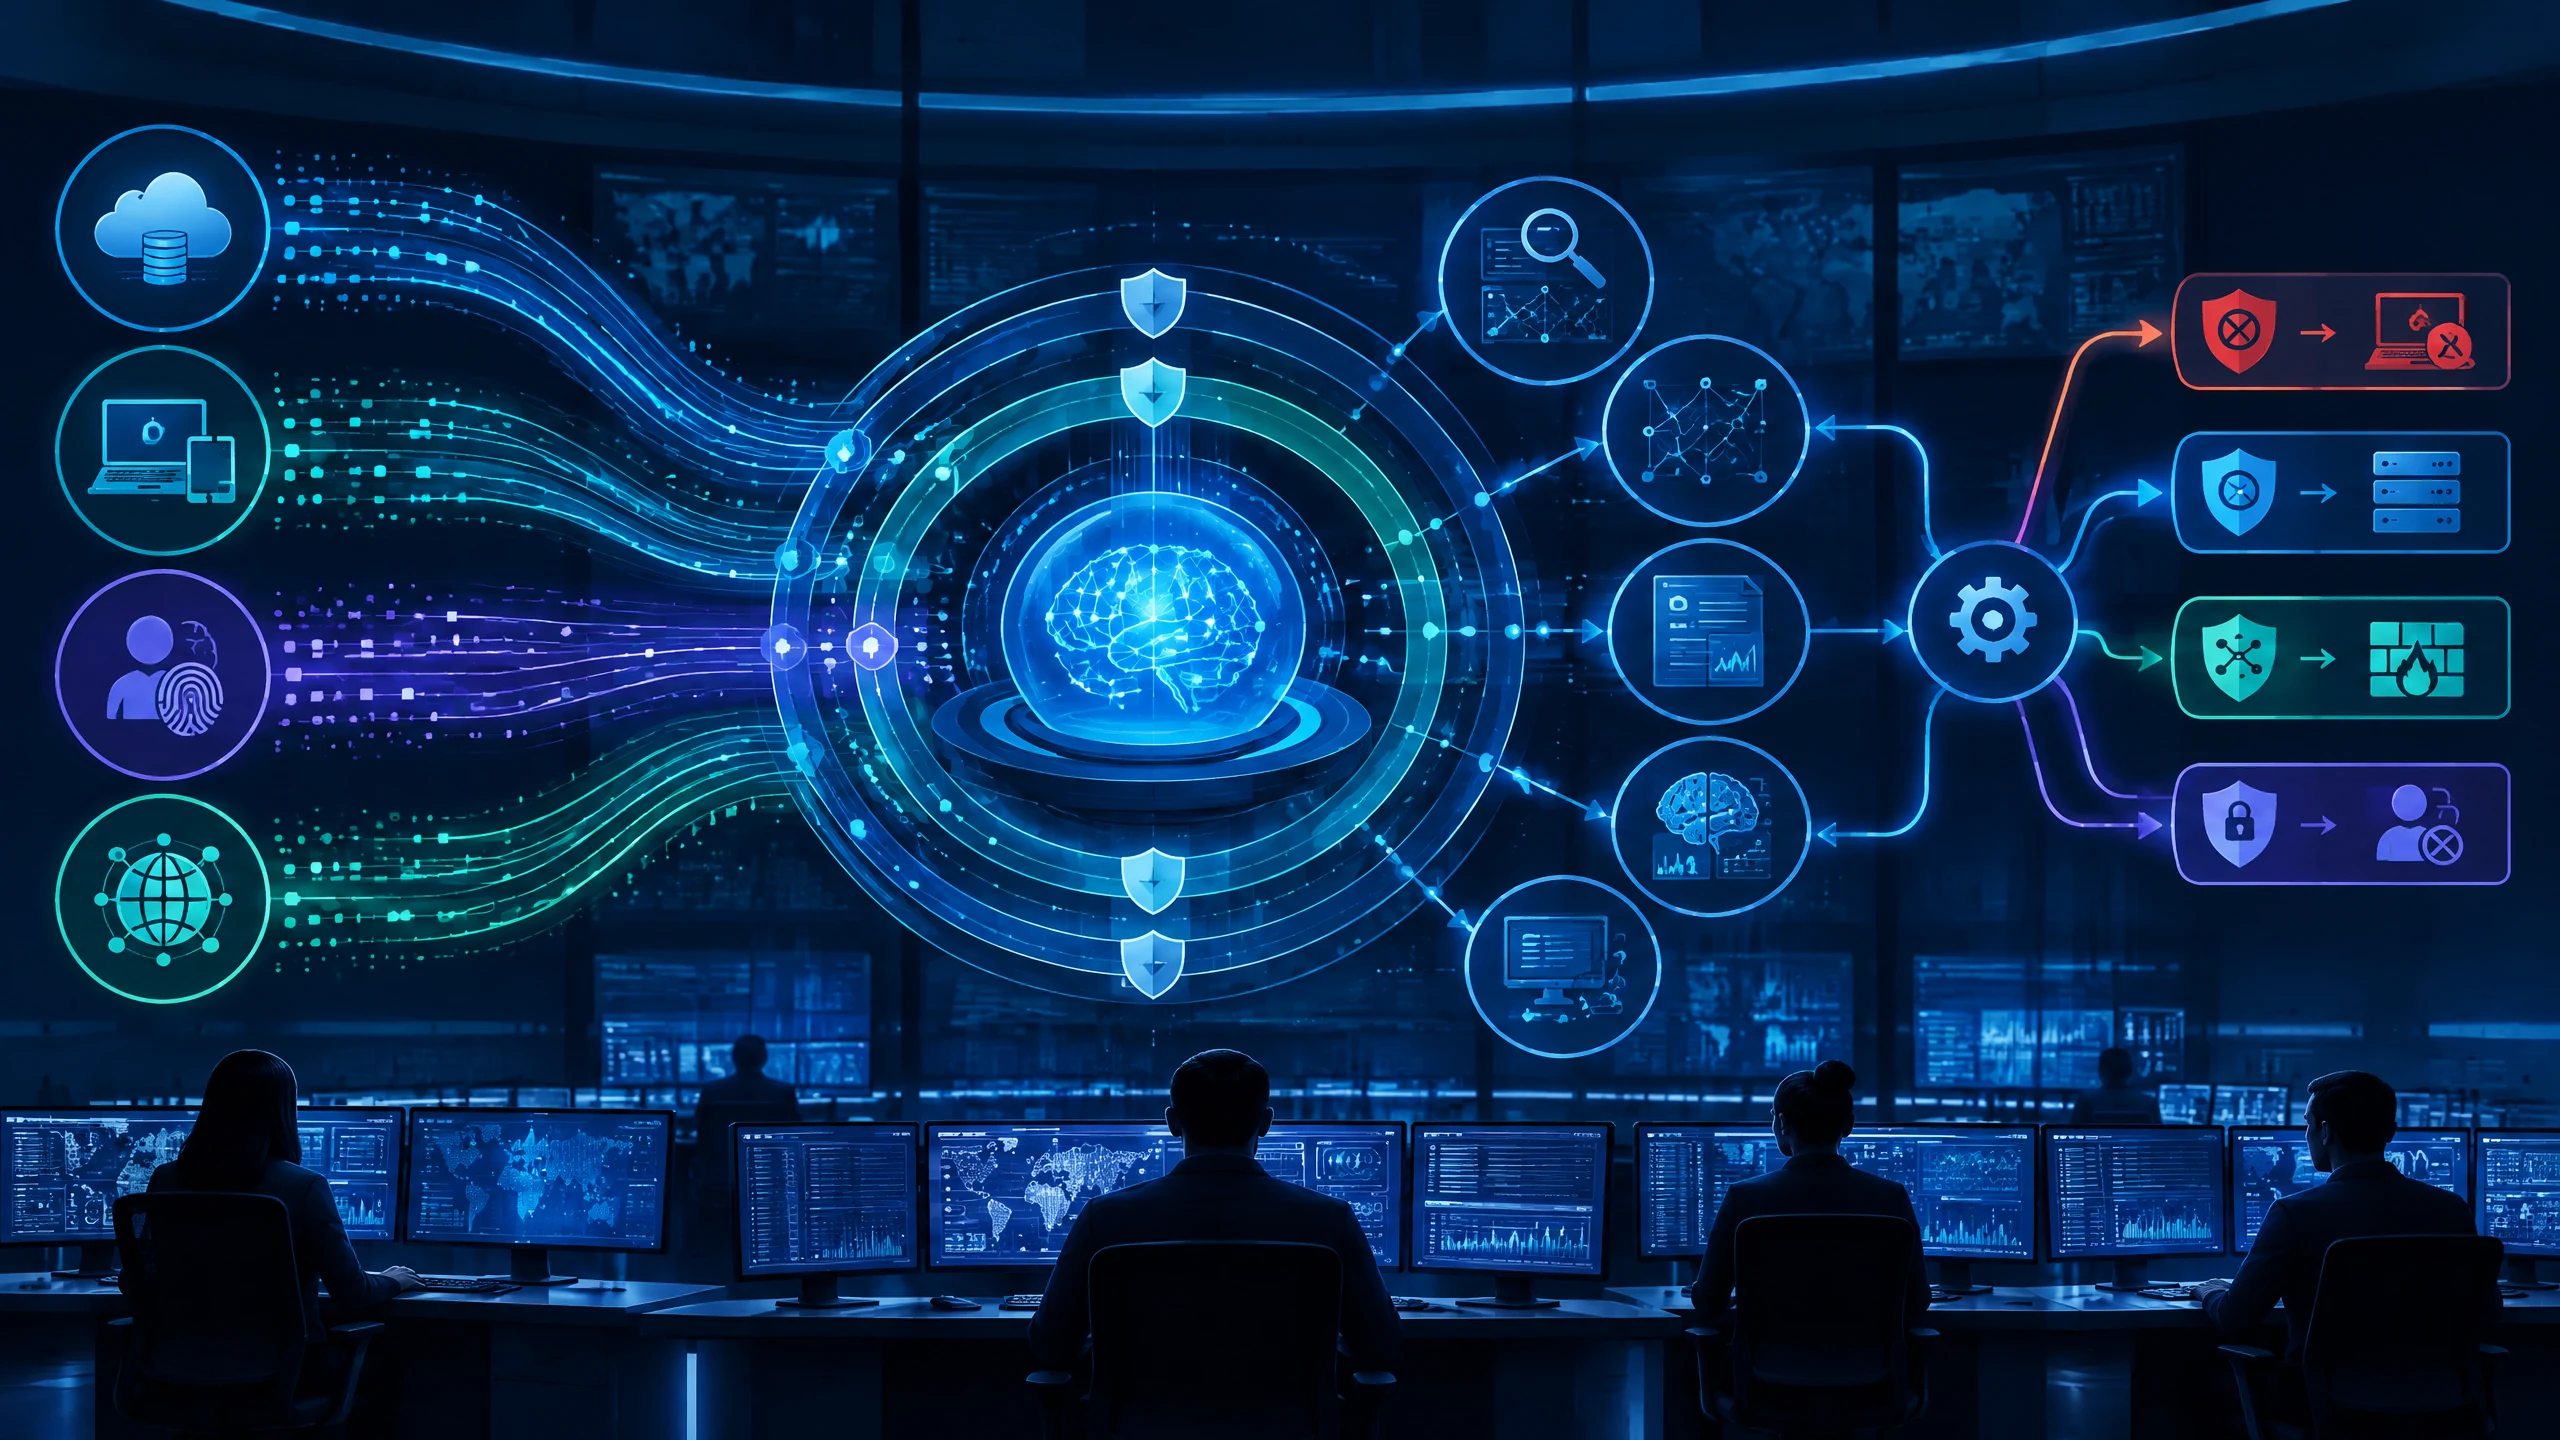
Security operations in 2026 work best as a coordinated system, not as a contest between acronyms. **SIEM provides broad event visibility and correlation, XDR connects detections across security layers, and SOAR orchestrates repeatable response actions.** An AI-augmented SOC adds an analysis and assistance layer that can summarize evidence, prioritize alerts, suggest investigative paths, and support threat hunting. It should not quietly make high-impact decisions without defined controls and human approval. This pillar-page explainer maps the pieces, compares them, and shows a seven-step defensive workflow. The goal is practical orientation rather than a product shortlist. **Key Takeaways** - SIEM is the broad collection, search, and correlation layer for security events and logs; XDR is a cross-layer detection and response approach; SOAR is the orchestration and workflow layer. - An AI-augmented SOC can reduce repetitive investigation work, but its output needs provenance, confidence, access controls, testing, and human approval for disruptive actions. - Alert fatigue is an operating-model problem as much as a tooling problem. Better signal quality, clear ownership, useful enrichment, and regular tuning matter more than simply adding more detections. - Threat hunting remains important because not every meaningful compromise begins as a high-confidence alert. Hunting should connect hypotheses to telemetry, identity, cloud, endpoint, and network evidence. - The most durable 2026 workflow is continuous: collect, detect, enrich, investigate, contain, recover, and learn.
What security operations means in 2026
Security operations is the continuous work of finding, understanding, containing, and learning from suspicious activity across an organization’s technology environment. That environment now commonly includes cloud services, software-as-a-service applications, remote endpoints, identities, APIs, containers, networks, and third-party connections. A SOC may be internal, shared, or supported externally. The principles remain visibility, analysis, coordinated action, and accountability.
The 2026 shift is toward **unified security operations**. Instead of treating endpoint, identity, cloud, email, and network alerts as separate queues, teams increasingly connect their evidence and cases. AI assistance is becoming part of that workflow. Terms such as *AI SIEM*, *agentic SOC*, and *autonomous SOC* describe systems that can perform multi-step analysis or propose actions. They do not remove the need for good telemetry, well-defined authority, or people who can challenge an incorrect conclusion.
NIST’s recent incident-response guidance emphasizes continuous risk management across governance, identification, protection, detection, response, and recovery. That framing is useful for SOC design because detection is not the finish line. A useful SOC turns findings into containment, recovery, lessons learned, and better controls. [Learn how the first hour of incident response is structured](/articles/incident-response-first-hour) when a suspected incident is moving quickly.
SIEM, XDR, and SOAR: what each one does
The three capabilities overlap, but they answer different operational questions.
### SIEM: What happened across the environment?
A security information and event management platform collects, normalizes, stores, searches, and correlates event data from sources such as identity systems, cloud control planes, operating systems, applications, network devices, and security tools. It can support rules, anomaly analysis, dashboards, investigations, compliance evidence, and long-term forensic searches.
SIEM is valuable when an investigation needs breadth. An analyst may need to connect a suspicious sign-in, mailbox rule, cloud permission change, endpoint process, and unusual data transfer. A well-run SIEM makes those clues searchable and supports detection tuning.
SIEM quality depends on more than collecting everything. Data needs useful timestamps, identity context, asset context, retention appropriate to the use case, and a clear understanding of what is missing. CISA’s SIEM and SOAR implementation guidance highlights the importance of prioritizing log sources rather than treating ingestion as an unlimited checklist.
### XDR: Is this activity a connected attack?
Extended detection and response, or XDR, connects telemetry and detection logic across multiple security layers. The emphasis is on cross-domain context: for example, linking an email lure to an endpoint process, a credential change, and suspicious network communication. XDR often presents related signals as an incident rather than as isolated alerts.
XDR can reduce analyst pivoting when sources are well integrated. Yet “extended” does not mean universal: coverage, retention, ownership, and integration depth vary. Treat an XDR view as available evidence, not proof that unconnected systems are clean.
### SOAR: What should happen next, and who approves it?
Security orchestration, automation, and response, or SOAR, coordinates tools and procedures through workflows called playbooks. A playbook can enrich an alert, retrieve related evidence, create a case, notify an owner, request approval, or carry out a narrowly defined containment action.
SOAR is strongest when the decision path is understood and repeatable. It can standardize phishing triage, suspicious-login enrichment, indicator checks, ticket creation, and evidence collection. The safest automation is not necessarily the most dramatic. It is the automation that is observable, reversible where possible, tested against edge cases, and clear about when a human must decide.
SIEM vs XDR vs SOAR: a simple comparison
| Capability | Primary question | Main input | Typical output | Best understood as |
|---|---|---|---|---|
| SIEM | What happened across many systems? | Logs, events, alerts, and context | Correlated searches, detections, timelines, and cases | The broad evidence and analysis layer |
| XDR | Are signals across security layers part of one threat? | Endpoint, identity, email, network, cloud, and other telemetry | Connected incidents, detections, investigation context, and response options | The cross-layer detection and response view |
| SOAR | What repeatable action should follow a finding? | Alerts, cases, enrichment, and playbook conditions | Automated or approval-gated workflows and documented actions | The coordination and execution layer |
These are not mutually exclusive choices. A SOC may use SIEM for retention, XDR for connected detections, and SOAR for response coordination. Combined platforms can simplify workflows, but the team must still explain evidence, conclusions, and automation authority.
The AI-augmented SOC: assistance before autonomy
An AI-augmented SOC uses machine learning, generative AI, or agentic systems to help people work through security data and procedures. Common assistance includes summarizing timelines, grouping alerts, suggesting queries, extracting indicators, comparing behavior with a baseline, drafting reports, and proposing investigative steps.
An **agentic SOC** goes further by allowing an AI system to plan and execute a sequence of bounded tasks. For example, an agent may inspect an alert, retrieve identity and endpoint context, check approved intelligence sources, and prepare a case summary. The operational boundary matters: gathering evidence and drafting a recommendation are different from disabling an account, isolating a production server, deleting a cloud resource, or changing a firewall rule.
### Guardrails for useful AI operations
A practical AI operating model has five controls:
1. **Scope:** Give the system a defined set of data sources, tools, actions, and environments. Least privilege applies to AI agents as well as people.
2. **Provenance:** Preserve the events, queries, tool calls, and evidence behind a summary or recommendation. Analysts need to inspect the path, not just the answer.
3. **Confidence and uncertainty:** Show when the system is guessing, missing data, or working from conflicting signals. A fluent explanation is not the same as a verified conclusion.
4. **Human approval:** Require an explicit approval step for disruptive, irreversible, legally sensitive, or business-critical actions. Approval should be meaningful, not an automatic click-through.
5. **Evaluation:** Test prompts, playbooks, detections, and agents against benign edge cases, adversarial inputs, and known incident scenarios. Review failures and near misses.
AI also creates a new attack surface. Prompt injection in security tooling, poisoned context, excessive agent permissions, and unsafe tool calls can turn a helpful assistant into a path for manipulation. Keep the investigation context bounded and treat instructions found in untrusted content as data, not authority. The [AI security and prompt-injection overview](/articles/ai-security-prompt-injection) provides useful context for this distinction.
A seven-step defensive security-operations workflow
This tool-neutral workflow can use different combinations of SIEM, XDR, SOAR, case management, and human investigation.
### 1. Establish the operating context
Define the assets, identities, business services, data flows, and dependencies that the SOC is expected to protect. Record which systems are critical, which teams own them, and what actions are allowed during an incident. Without this context, a technically accurate alert may still receive the wrong priority.
### 2. Collect and normalize high-value telemetry
Start with decision-useful signals: authentication and privilege changes, endpoint activity, cloud control-plane events, email, network, application, and key data-access logs. Normalize time, identity, asset, and event fields. Review gaps deliberately; a smaller reliable data set can beat an uninterpretable stream.
### 3. Detect and group related activity
Use rules, behavioral analytics, threat intelligence, and detection engineering to identify suspicious patterns. Correlate related events into incidents so that analysts see a story rather than a pile of notifications. Tune for both precision and coverage. A detection that fires constantly without useful context contributes to alert fatigue and eventually loses attention.
### 4. Enrich and triage
Add identity history, asset criticality, recent changes, vulnerability context, known indicators, and related cases. Separate “interesting” from “urgent.” AI can summarize and suggest pivots here, but the summary should link back to source evidence. Route the case to an owner with a clear service level and escalation path.
### 5. Investigate and hunt
Test a hypothesis across the relevant telemetry. Look backward for the first suspicious activity and forward for persistence, privilege escalation, lateral movement, or data access. Threat hunting is not random searching; it is a structured attempt to find activity that existing detections may have missed. For cloud investigations, include identity, permissions, network security, and control-plane changes. [Review common cloud misconfiguration risks](/articles/cloud-misconfiguration-risk) that can create misleading or high-impact signals.
### 6. Contain and respond with approval gates
Use predefined playbooks for repeatable actions, such as collecting evidence, revoking a session, blocking a confirmed indicator, or opening a coordinated incident. Put human approval before actions that could interrupt services or affect many users. Document who approved what, which evidence supported the decision, and how the action can be reversed. Identity-focused events deserve particular care; [MFA-bypass and identity attack patterns](/articles/identity-attacks-mfa-bypass) illustrate why a single login signal rarely tells the whole story.
### 7. Recover, measure, and improve
Confirm containment, restore services safely, and monitor for recurrence. Close the case after recording evidence, decisions, notifications, and owners. Feed lessons into detections, access, logging, playbooks, and training. Measure meaningful triage time, investigation quality, containment confidence, repeat incidents, and automation failures—not just alert counts.
Threat hunting, alert fatigue, and human judgment
Alert fatigue is often described as a volume problem, but it is also a trust problem. Analysts become overloaded when alerts lack context, ownership is unclear, severity is inconsistent, and closing a case does not improve the system. Better practices include grouping duplicates, suppressing known benign patterns with an expiry date, enriching alerts before assignment, measuring false-positive causes, and retiring detections that no longer support a decision.
Threat hunting balances this reactive queue. It asks what an attacker could do that current alerts might not reveal. Hunts can focus on unusual identity behavior, administrative changes, new persistence, unexpected remote tools, suspicious cloud activity, or data movement. Ransomware response guidance, for example, connects containment with hunting for precursor activity and lateral movement rather than treating encryption as the beginning of the story. See [ransomware attack paths and their common stages](/articles/ransomware-attack-paths) for a related defensive lens.
Human judgment remains essential where context is incomplete or the cost of a wrong action is high. AI can make the analyst faster; it cannot be the sole source of accountability for a decision that affects safety, availability, privacy, or evidence. A supportive SOC culture makes it acceptable to question an AI recommendation, request more evidence, and pause an automation that behaves unexpectedly.
What to prioritize when modernizing a SOC
Modernization begins with operating clarity, not a tool shopping list. Define important incidents, needed evidence, and authorized actions. Improve the data pipeline and a few high-value detections, then automate stable work before attempting broad agentic autonomy.
Measure whether analysts reach defensible conclusions with less friction. Review investigation completeness, enrichment, repeated manual steps, missed context, approval quality, and cross-domain coverage.
The 2026 direction is continuous evidence interpretation and response coordination, with AI performing more bounded work. The destination is not “no humans,” but less console copying and more hypothesis testing, risk decisions, control improvement, and clear communication. The [AI security topic hub](/topics/ai-security) provides adjacent reading for those operating concerns.
Frequently asked questions
### Does XDR replace SIEM and SOAR?
Not automatically. XDR may combine some collection, correlation, and response features, but organizations still need broad log retention, search, governance, integrations, or specialized workflows that an XDR view may not provide. The right architecture depends on coverage, data requirements, existing processes, and how clearly responsibilities are defined.
### Is an AI SOC fully autonomous?
The phrase is used inconsistently. Some systems automate enrichment and routine triage; others can plan and execute multiple actions. “Autonomous” should describe a specific authority boundary, not imply that human accountability has disappeared. High-impact actions should remain approval-gated and auditable.
### How does SOAR reduce alert fatigue?
SOAR can reduce repetitive work by enriching alerts, grouping evidence, assigning cases, and executing repeatable steps. It does not fix poor detection logic by itself. If a workflow automates noisy alerts without improving signal quality, it may simply create faster noise.
### What makes a good threat-hunting program?
A good program has a defined hypothesis, relevant telemetry, a repeatable query or method, documented findings, and a path to improve detections or controls. Hunts should be prioritized by plausible attack paths and business impact, not by novelty alone.
### Why is human approval important in an AI-augmented SOC?
Some actions can disrupt services, lock out users, destroy evidence, or create legal and operational consequences. Human approval provides a deliberate decision point, especially when evidence is ambiguous or the action is difficult to reverse. Approval works best when the reviewer receives concise evidence, uncertainty, proposed impact, and rollback information.
Conclusion
Security operations in 2026 are becoming more connected and more assisted by AI, but the fundamentals remain stable. SIEM helps teams collect and correlate broad evidence. XDR connects security-layer signals into a more coherent detection and response view. SOAR turns repeatable decisions into visible, governed workflows. AI can reduce investigation friction and help analysts hunt more effectively when its access, evidence, confidence, and authority are controlled.
A resilient SOC treats these capabilities as parts of one defensive workflow: understand context, collect useful telemetry, detect and group activity, enrich and triage, investigate, contain with approval, and learn. That approach supports faster work without confusing speed with certainty.
Limitations
- Guidance and regulations can change; verify current advisories and organizational applicability before acting.
Evidence sources
- cisa.gov — Cybersecurity and Infrastructure Security Agency (CISA), “New Guidance for SIEM and SOAR Implementation” (May 27, 2025)
- nvlpubs.nist.gov — National Institute of Standards and Technology (NIST), “SP 800-61 Revision 3: Incident Response Recommendations and Considerations for Cyber Risk Management” (2025)
- microsoft.com — Microsoft Security, “What is SOAR?” (updated May 26, 2026)
- paloaltonetworks.com — Palo Alto Networks Cyberpedia, “What Is SOAR vs. SIEM vs. XDR?”
- cisa.gov — Cybersecurity and Infrastructure Security Agency (CISA), “StopRansomware Guide”